Compliance as a Service
Compliance handled. Growth unlocked.
Most companies treat compliance as a tax on growth. We turn it into an asset — a complete program we build for you and keep running, so your team can focus on the work only they can do. A little magic for what’s next.
Seattle & Gothenburg — one firm, two continents, US and EU readiness built in.
Your entire compliance function, delivered
One partner for the full suite — from first assessment to certification and everything after.
Privacy & data protection
GDPR, CCPA, and cross-border data transfers handled end to end — from records of processing to DPIAs and breach response plans.
Certification readiness
ISO 27001, SOC 2, and industry frameworks — we build the controls, gather the evidence, and walk you through the audit.
Policies & documentation
Clear, usable policies your team will actually follow — not binders that gather dust. Written for humans, defensible for auditors.
Risk & vendor management
Structured risk assessments and a vendor review process that keeps third parties from becoming your weakest link.
Training & awareness
Practical training that sticks, tailored to your teams — so compliance becomes habit, not homework.
Ongoing maintenance
Regulations move. We monitor changes, update your program, run internal audits, and keep you continuously ready.
Why compliance matters
Done poorly, compliance is a cost center. Done well, it opens doors.
Win bigger deals
Enterprise buyers ask hard questions before they sign. A mature compliance program turns security reviews from deal-killers into fast passes.
Enter new markets
From the EU to the US, every market has its own rulebook. Being compliant on day one means you expand on your timeline, not a regulator’s.
Avoid fines & firefighting
Penalties, breach costs, and emergency remediation are far more expensive than doing it right. Prevention is the cheapest strategy there is.
Earn lasting trust
Customers, partners, and investors reward companies that take their obligations seriously. Trust compounds — and it starts with the fine print.
How working with us works
A simple engagement, whether we run everything or slot in beside your team.
Assess
We map where you stand today: your data, your obligations, your gaps. You get a clear, prioritized picture — no jargon, no scare tactics.
Build
We design and implement your full compliance suite: policies, controls, processes, and evidence — tailored to your size and your market.
Maintain
On an ongoing retainer, we keep everything current: monitoring regulatory change, running reviews, answering questionnaires, and standing by your side in audits.
Two continents. One firm.
With a foot in Seattle and a foot in Gothenburg, we work inside both regulatory worlds every day — not as an occasional specialty. Our teams overlap across US and EU time zones, so wherever your customers wake up, we’re already working. Expanding in either direction, you get readiness for both markets from a single partner.
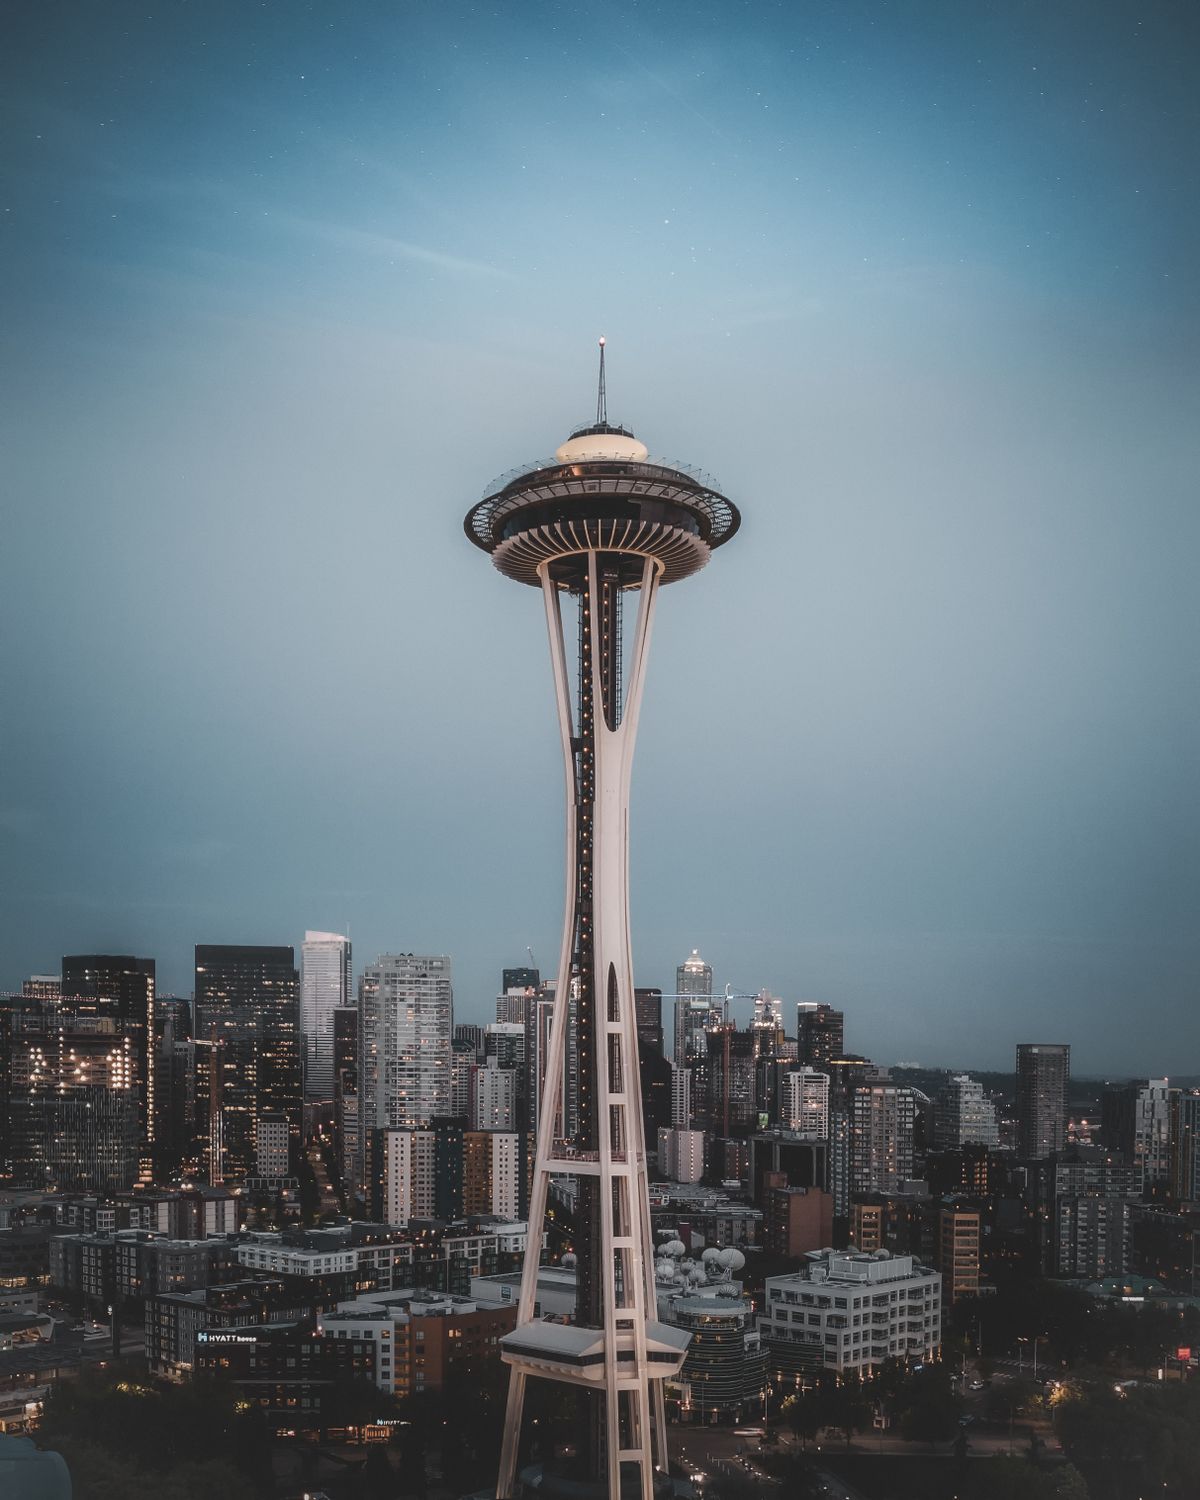
US readiness
The American market runs on trust signals: SOC 2 reports that pass enterprise procurement, a defensible position on the growing patchwork of state privacy laws — CCPA/CPRA and the states following it — and the sector rules that apply to your industry, HIPAA included if you touch health data. We get you deal-ready for US buyers.
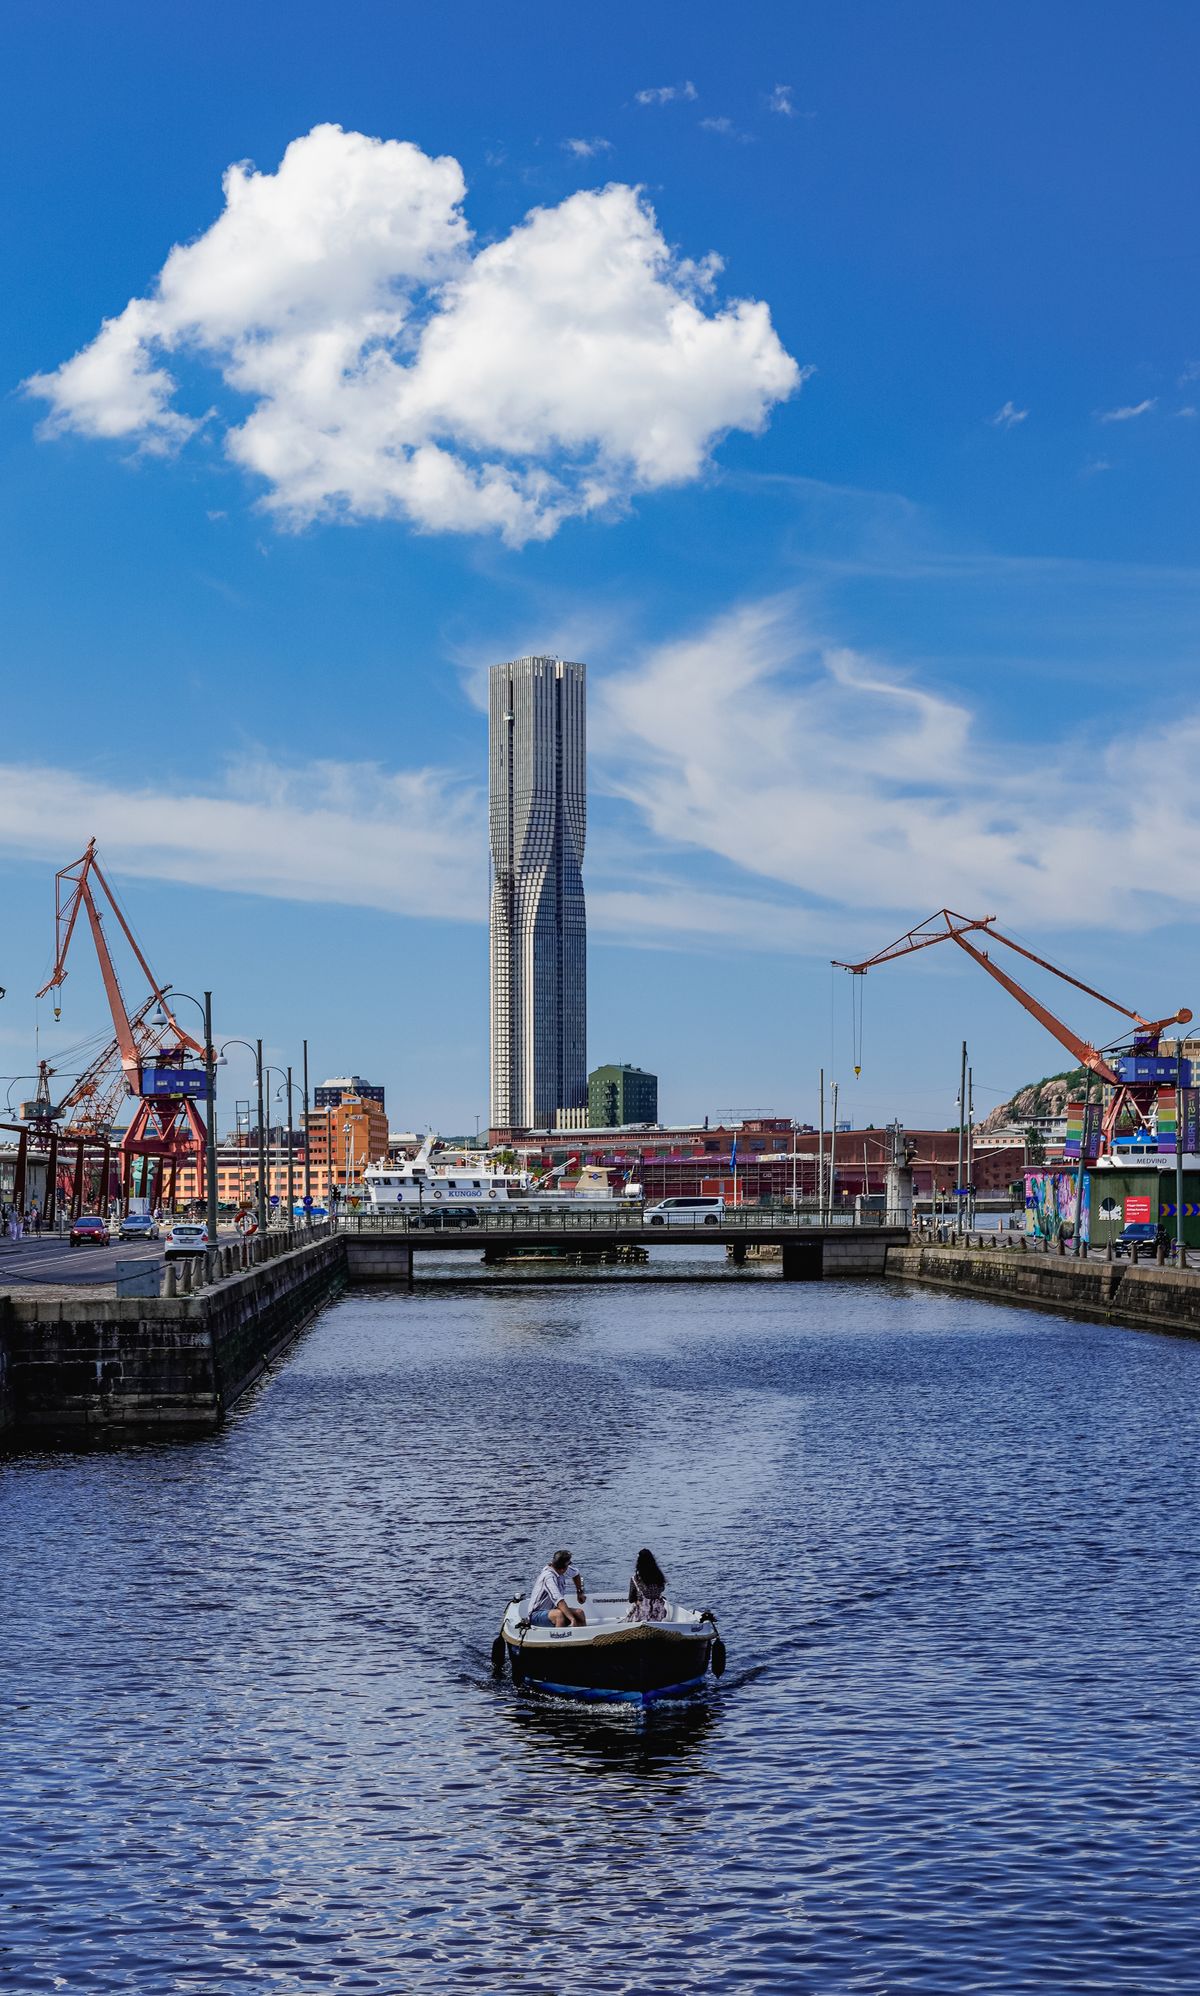
EU readiness
Europe expects substance: GDPR done properly, ISO 27001 where buyers ask for it, and a clear line on the new wave — NIS2, DORA, and the EU AI Act. We build programs that satisfy European regulators and customers alike, including cross-border data transfers that hold up.
Work with us once — be ready on both sides of the Atlantic.
Built for teams of every size
Small teams
No compliance hire, no problem. We become your compliance function — setting up the full program and running it month after month for a fraction of the cost of a full-time role.
Established organizations
Already have a team but need more hands or deeper expertise? We plug into your existing structure — taking on audits, certifications, or the backlog your team hasn’t had time to reach.
Ready to make compliance your advantage?
Tell us where you are and where you’re headed. We’ll show you the shortest path to getting — and staying — compliant.